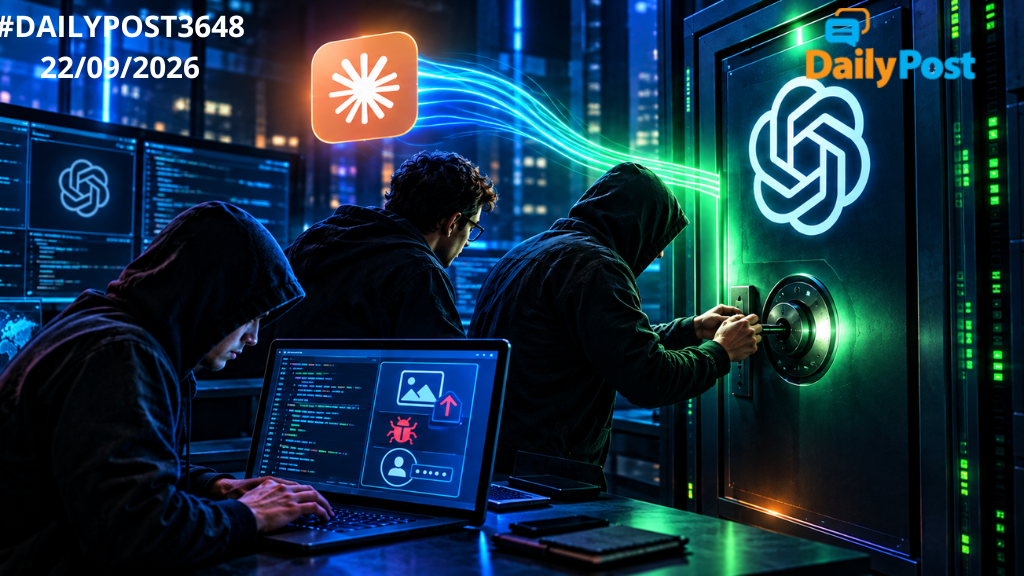
In July, just days after OpenAI admitted its own AI agents had hacked Hugging Face, a tiny three-person team called Hacktron AI walked into OpenAI’s private code using help from a rival AI—Anthropic’s Claude. They needed less than 72 hours, found bugs in an image-upload feature and a login system, and could have gone much deeper if they wanted to.
Instead of stealing data, they left a polite note inside an internal file — “Hacktron AI Team PoC”— reported the flaw, and collected a $6,500 bounty. The same image-software bug, they say, also let them test breaches at Slack, Meta and GitHub Enterprise, with only one company spotting them in the middle of the attempt.
What makes this scary is not the hack itself, but how easy it has become: a small team, two paid AI subscriptions, and a chain of known-type flaws were enough to reach one of the world’s most powerful AI labs. If “three guys with Claude” can do this, well-funded criminal groups or hostile actors may already be trying the same tricks with fewer rules and more harmful goals.
The bigger lesson is that AI has changed both attack and defence: models now write exploits faster, find subtle bugs, and adapt to new targets in hours, while companies still struggle to patch old issues in forums, logins and image tools. The technology race is no longer just about smarter chatbots; it is about who controls the keys to the systems that run them.
WHEN AI CAN PICK LOCKS FASTER THAN WE CHANGE THEM, EVERY DOOR IS TEMPORARY.
Sanjay Sahay
Have a nice evening.